BreakMi: Reversing, Exploiting & Fixing Fitness Tracking Ecosystems
summary
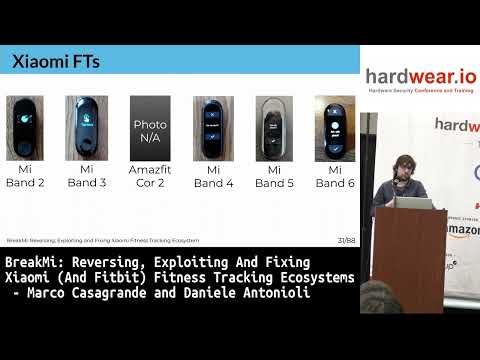
Reverse engineering finds Xiaomi trackers since 2016 use vendor‑specific application protocols over BLE with link‑layer security disabled, and authentication is unilateral and replayable. The team develops and open‑sources BreakMi toolkit (Node.js bleno/noble modules plus an Android component) and demonstrates six practical attacks: four allow wireless impersonation, MitM and eavesdropping, two let a malicious Android app exfiltrate and take over devices. Tests cover six devices (2016–2021) and live demos and automated exploits succeed; five low‑overhead mitigations are proposed.
AI-written summary · about
chapters (15)
- 0:00Introduction and context
- 1:30Ecosystem and BLE protocol
- 5:38Security risks and analysis
- 7:31Reverse engineering methods
- 12:18Xiaomi security evaluation
- 14:01Xiaomi pairing and auth
- 17:24Proximity attacks
- 20:05Remote attacks
- 22:20Attack results and setup
- 24:38The toolkit and setup
- 27:09Live demo and MITM
- 31:43Remote attack demo
- 33:20Fitbit security analysis
- 36:15Countermeasures and disclosure
- 39:00Q&A and conclusion
related talks
 30mUnfit Story of Fitness Trackers: Hacking BLE Fitness Trackers
 52mIoT Hacking 101: Reverse Engineering The Xiaomi Ecosystem
 30mUnfit Story of Fitness Trackers: Hacking BLE Fitness Trackers
 51mBluetooth Hacking: Tools And Techniques
 24mAttacking Bluetooth LE Design and Implementation in Mobile + Wearables Ecosystems
 35mDeep into Android Bluetooth Bug Hunting: New Attack Surfaces and Weak Code Patterns
 18mE-Trojans: Ransomware, Tracking, DoS, and Data Leaks on the Xiaomi E-Scooter...
 25mSweynTooth: Unleashing Mayhem over Bluetooth Low Energy