The Death Star and the Ultimate Vulnerability

summary
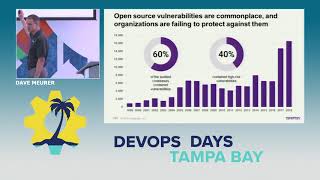
Modern apps run on Software Composition Analysis and SBOM practices because roughly 90% of production code is open source and an average Java project pulls ~150 dependencies (≈1,500 releases to track). A single Java supply‑chain flaw racks up tens of millions of downloads — one vulnerable jar hits ~51 million downloads in six months with ~33% of downloads using the insecure version. Use scorecards, continuous scanning, branch protection and Maven Central controls to locate, monitor and remediate affected components.
AI-written summary · about
chapters (17)
- 0:00Introduction to talk
- 1:05Open source and security risks
- 3:34History and rise of open source
- 7:08Death Star parallels to software
- 9:18Cybercrime financial impact
- 12:51Open source in critical systems
- 14:17Legislation and liability in software
- 16:47Software licensing changes
- 19:36Software composition analysis
- 21:42Software bill of materials
- 23:44Open source project health
- 25:54Vulnerability management
- 27:18Open source repository attacks
- 29:25Log4j vulnerability case study
- 30:49Best practices for secure development
- 32:57Lifecycle monitoring in software
- 33:39Conclusion and final thoughts
related talks
 21mWhy Building Your Ship (Application) with Raw Materials is a Bad Idea!
 32mAdapting DevOps in a World of Growing Software Supply Chain Attacks
 48mCommon vulnerabilities you wish your Java app didn't have!
 41mThe Divine and Felonious Nature of Cyber Security
 30mDevSecOps: Understanding Open Source Software risk in your applications
 48mAn Introduction to the Newest Addition to the OWASP Top 10
 31mOpen Source Supply Chain Threat Landscape - A Moving Target
 46mStrengthening Java Apps: Best Practices in Secure Coding for Java Developers