Magic of ADB
summary
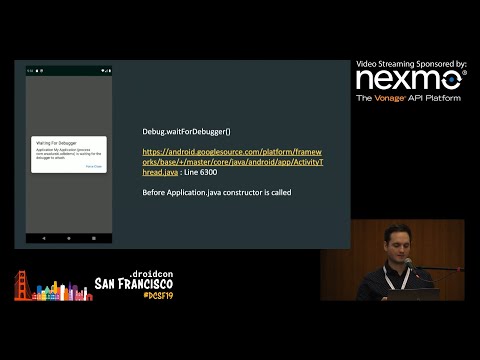
ADB runs as an init-started native daemon communicating with an ADB server on localhost:5037 and uses JDWP threads to expose debugable app processes so Android Studio can track JDWP and offer apply changes; starting with the debug flag boots the app into activity thread before any app code runs, attaching alone does not. Emulators run ADB insecure (allowing adb root and remount rw to preinstall system APKs), real devices don’t; surprising counts: plain builds show 13 threads per app, ~165 system services on modern emulators, and tools used include toybox, dumpsys and scrcpy for screen mirroring.
AI-written summary · about
chapters (15)
- 0:00Introduction to ADB
- 1:18How ADB installs apps
- 6:21Debugging with JDWP
- 9:54ADB vs SSH
- 14:30ADB at boot time
- 17:46ADB root and remounting
- 19:12Android shell and Toybox
- 23:07Exploring Android file system
- 27:30Extracting framework.jar
- 28:58System services and Binder
- 31:07Processes and Zygote
- 33:38Threads in Android apps
- 36:37Advanced debugging tools
- 37:42Dumpsys for system state
- 40:13Closing remarks and book recommendation
related talks
 47mMagic of ADB and Android shell
 42mADB Break on through to the other side
 50mADB, Break On Through To the Other Side
 47mAndroid Debug Bridge: Step to the Other Side of the Black Mirror
 41mExploring Android internals with ADB
 01h 02mAndroid Platform Debugging and Development
 20mLife is too short not to use ADB commands
 21mWhat if ADB does not have to be that complicated?