The Anatomy of a Hack 24 Hours in the DevSecOps ER
summary
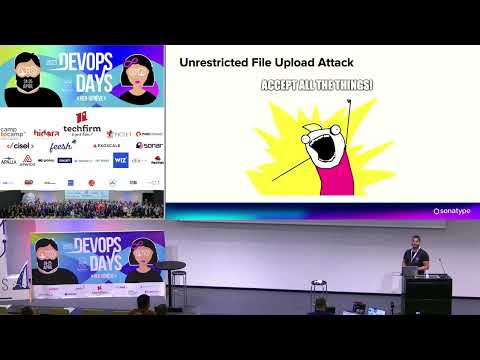
Forbes finds 83% of SMBs feel unprepared and this recounts a WordPress site defacement that overwrote keys and left no backups, forcing a full rebuild; logs reveal requests to flickr.mydomain.com that upload a PHP file via TimThumb RCE via fake image magic bytes, allowing remote code execution and server takeover. Recovery takes weeks; remediation uses log forensics, hardening upload perms (no 777), dependency pinning, OWASP ZAP in Jenkins scans, threat modeling, branch protection and code review to prevent recurrence.
AI-written summary · about
chapters (19)
- 0:00Security introduction
- 1:48Why security matters
- 4:56Defacement incident begins
- 7:05Website compromised
- 9:18Investigating via logs
- 10:46TimThumb vulnerability
- 13:20Exploit bypassed checks
- 15:29Incident response recovery
- 16:12Lessons from breach
- 17:35Access control permissions
- 19:23PHP vulnerabilities critique
- 20:29Secure coding practices
- 21:34DevSecOps branch protection
- 22:17Dependency scanning tools
- 23:00Q&A commit security
- 25:34Security champions design
- 28:08Post-attack changes
- 30:57Security tools strategies
- 32:01Summary
related talks
 44mI've Been Hacked, Now What
 40mHow to hack a node app?
 43mI Had WordPress, but It Got Hacked
 38mHackers Gonna Hack: Identifying and Fixing Vulnerabilities Proactively
 47mLive Hacking: Breaking into Your Web App
 41mLive Hacking: Breaking into Your Web App
 39mHow to think like a hacker
 01h 01mHow hacking works - Web edition