Surfacing from the Underbrush: Machete Pivots to Intrusion-Enabled Info Ops
summary
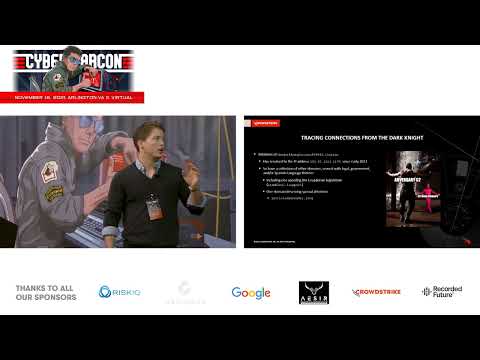
June 2021 malware-laced Office macros deliver a Python backdoor known as Ragwa RAT aka Machete, and passive DNS links the dropper domain thedarkknightrises.number.online / justiciamorada.org to a cluster of Spanish‑language domains hosting allegedly stolen Ecuadorian judicial files; registration and Cloudflare name‑server patterns tie those domains to the same operator behind the innopapers.org leak, 2019. Analysis shows reuse of decoy stolen documents for phishing, modular malware updates, and presents an attribution case for a nexus to the Colombian government.
AI-written summary · about
chapters (6)
- 0:00Threat actor Machete intro
- 1:47Machete's tactics and targets
- 2:532021 Ecuador election intrusion
- 4:36Justiciamorada smear campaign
- 7:06Innopapers scandal aftermath
- 8:29Colombian govt attribution
related talks
 17mRadRAT: An all-in-one toolkit for complex espionage ops
 33mOperation GamblingPuppet: Analysis of a Multivector and Multiplatform Campaign Targeting Online ...
 47mDetecting and analyzing files-less malware
 31mHacking People’s Mind: When Threat Actors Master Social Engineering
 26mThe Secret Life of Sandworms
 19mOperation PZCHAO
 47mWhen Governments Attack: State Sponsored Malware Attacks Against Activists Lawyers and Journalists
 26mTracking the World's Dumbest Cyber Mercenaries