Detecting and analyzing files-less malware
summary
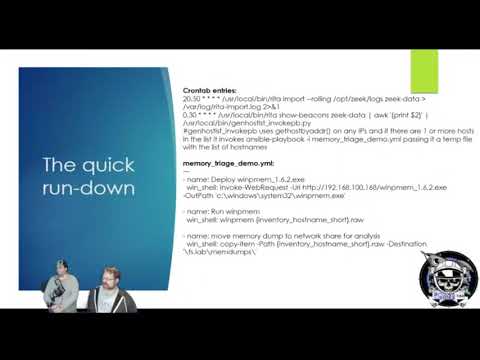
Network logs show two infected hosts (192.168.100.181 and .180) beaconing to C2, with RITA + Zeek flagging 3,129 unique subdomains under evil.lab as DNS tunneling. Automation kicks off a SOAR/Ansible playbook that deploys winpmem via Ansible to grab memory, moves dumps to a share, and provides PCAPs. Volatility plus YARA locates the malicious process, extracts VAD/memdumps and registry/task persistence artifacts, and confirms DNS and HTTPS beaconing enough to drive blocking and further reverse engineering.
AI-written summary · about
chapters (8)
- 0:00Start
- 0:57Define Fileless Malware
- 11:00Memory Triage Demo
- 12:50Indicators of Compromise
- 13:38Performing Memory Forensics
- 15:03Mem Dump
- 38:06Memory Analysis
- 42:00Tools Used
related talks
 33mBasic Malware Analysis for Incident Responders
 17mRadRAT: An all-in-one toolkit for complex espionage ops
 26mTracking the World's Dumbest Cyber Mercenaries
 47mWorm Charming: Harvesting Malware Lures for Fun and Profit
 59mCatching Malware En Masse: DNS and IP Style
 33mOperation GamblingPuppet: Analysis of a Multivector and Multiplatform Campaign Targeting Online ...
 22mMalware Hunting - Using python as an attack weapon
 42mWho Let the Dogs Out? When PUPs Become BlackCat's Best Friend