Ambient Mesh: new sidecar less & faster Istio for zero trust

summary
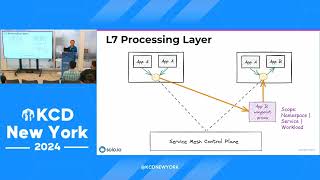
Claims a sidecarless Istio that keeps mTLS and policy control by splitting L4 and L7: a lightweight ztunnel (Rust) handles mTLS, L4 auth and encapsulates traffic via HBone on port 15008, while optional Waypoint Envoy pods handle L7. Demo installs Istio 1.18.3 on AKS two‑node cluster, labels namespaces (no pod spec changes), shows encrypted traffic vs plaintext, enforces L4 deny‑all then allow specific service accounts, applies L7 policy to allow only GET, runs a 90/10 canary ≈91/9, and uses Prometheus/Grafana/Kiali for observability.
AI-written summary · about
chapters (20)
- 0:00intro
- 0:27preamble
- 0:53about us
- 1:09agenda
- 1:47istio
- 2:10istio service mesh architecture
- 3:07limitations of sidecar
- 4:16let's break it down!
- 4:44the ambient mesh
- 5:54https connect tunnel
- 7:07is ztunnel truly secure?
- 10:32benefits of ambient mesh
- 11:37demo:
- 16:24install istio with ambient mesh
- 17:35enable ambient mesh
- 19:44apply l4 authorization policies
- 23:17allow traffic through ingress gateway
- 32:36traffic management: canary release
- 36:54observability and debugging
- 42:05good job
related talks
 37mDemystifying Secure Application Communication with Zero Trust and Istio Without Sidecars
 30mEmbracing the Future: The Effortless Mutual TLS and Traffic Control Without Sidecars
 32mEmbracing the Future: The Effortless Mutual TLS and Traffic Control Without Sidecars
 22mIs Istio Ambient Mesh Secure?
 29mZero Trust for APIs: From Edge to Mesh with Istio
 31mTrust no one: implementing zero trust security with Ambient Service Mesh
 11mIstio Ambient Mesh: Sidecar vs Sidecar-less, Explained Simply
 38mEmbracing the Future: The Effortless Mutual TLS and Rich Layer 7 Authz Policy Without Sid...