The Spear to Break the Security Wall of S7Commplus
summary
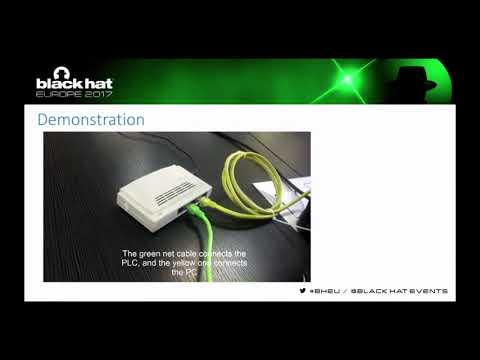
Demonstrates a practical break of S7CommPlus by reverse‑debugging the Siemens client binary to recover three proprietary encryptions, one simple XOR chain and a session‑ID based function cipher, then implements those routines in a small program and uses Wireshark captures to control an S7‑1200 (HW v4.1) PLC (stop/run shown). Replay attacks originally fail until the ciphers are reproduced. Suggests fixes: anti‑debug, optional PLC password and full‑packet encryption.
AI-written summary · about
chapters (8)
- 0:00Introduction and overview
- 2:31Understanding PLC protocols
- 5:39Analyzing compressed protocols
- 9:41Decrypting proprietary methods
- 12:18Demonstration of control
- 15:03Communication process summary
- 17:26Proposed security protections
- 18:43Q&A session
related talks
 29mFuzzing and Breaking Security Functions of SIMATIC PLCs
 39mA Decade After Stuxnet: How Siemens S7 is Still an Attacker's Heaven
 44mRogue7: Rogue Engineering-Station Attacks on S7 Simatic PLCs
 51mIndustrial Control Systems : Pentesting PLCs 101 (Part 2/2)
 58mIndustrial Control Systems : Pentesting PLCs 101 (Part 1/2)
 40mHacking Mitsubishi PLC Without Access To Firmware
 48mDoors of Durin: The Veiled Gate to Siemens S7 Silicon
 55mPLC-Blaster: A worm Living Solely In The PLC