Break Out of The Truman Show: Active Detection and Escape of Dynamic Binary Instrumentation

summary
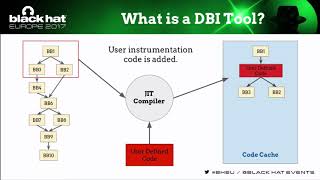
Shows concrete, reproducible DBI detection and full escape techniques against Pin and DynamoRIO: uses far-return/32↔64 cross‑mode switch to force a native 64‑bit decoder, finds Pin’s code‑cache signature (0xfeedbeef) and duplicated code pages, reads TSS/TLS slots and EBX backup at fixed offset to fingerprint DBI, and modifies code‑cache/stack/callback tables to hijack control flow. Demonstrates PMU-based traces that distinguish instrumented vs native runs and a working demo that disables DBI inspection.
AI-written summary · about
chapters (13)
- 0:00DBI detection and escape intro
- 2:07DBI architecture overview
- 3:10Past DBI detection research
- 3:54Passive DBI detection
- 7:34Active DBI detection
- 12:38Code cache signature detection
- 16:28TLS and EBX context detection
- 22:34DBI escape concepts
- 26:57Hardware monitoring for escape
- 30:54DBI escape criteria
- 33:23Function call counter demo
- 39:51Live DBI escape demo
- 42:14Security implications
related talks
 24mDefeating the Transparency Feature of DBI
 40mDynamic Binary Instrumentation Techniques to Address Native Code Obfuscation
 55mHiding PIN's Artifacts to Defeat Evasive Malware
 20mBluePill: Neutralizing Anti-Analysis Behavior in Malware Dissection
 25mPindemonium: A DBI-Based Generic Unpacker for Windows Executable
 30mEvasive Maneuvers: Strategies to Overcome Runtime Detection Tools
 51mMaking the most of Security Tests
 45mThe Container Escape Room: An Exploration of Container Escapes