Client-Side Protection Against DOM-Based XSS Done Right (tm)
summary
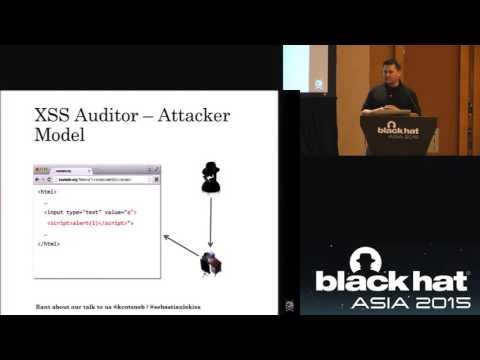
Analysis finds 17 Chrome XSS Auditor flaws and a bypass toolkit that auto-generates exploits; running those probes against the Alexa Top 10k uncovers about 1,600 unique DOM‑XSS vulnerabilities on 958 domains and a successful Auditor bypass on first try for over 80% of vulnerable sites. Client‑side defenses switch to byte‑level taint‑tracking in the JavaScript engine that blocks tainted inputs becoming identifiers or external includes, with low false positives (0.016% frames) and prototype overheads around 7% average (up to ~17% in worst typical cases).
AI-written summary · about
chapters (9)
- 0:00Introduction and background
- 1:40Understanding XSS attacks
- 5:10Client-side XSS defenses
- 9:14Evaluation of XSS filters
- 11:47How the XSS auditor works
- 19:01Auditor bypass techniques
- 33:37Proposed new filter design
- 38:11Evaluation and conclusion
- 44:55Q&A session
related talks
 40mClient-Side Protection Against DOM-Base...
 55mCall To Arms: A Tale of the Weaknesses of Current Client-Side XSS Filtering
 42mDon't trust the DOM: Bypassing XSS mitigations via script gadgets
 41mThe Insecurity Caused By Trusting Your Client-Side Storage
 42mEverything you need to know about client-side malicious code execution
 52mDemystifying Front-End Security
 23mJavaScript attack surface
 41mThe Last XSS Defense Talk: Why XSS Defense has radically changed in the past 7 years