API Deobfuscator: Identifying Runtime - Obfuscated API Calls Via Memory Access Analysis

summary
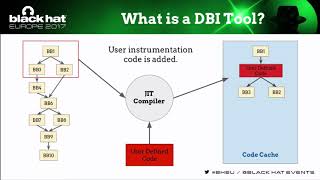
Builds a memory read/write map that links each original API function to the set of addresses written when that function is runtime‑obfuscated by Themida, then resolves call targets by matching obfuscated-call targets to that map. Implements the approach as an Intel Pin tool, records reads on API code and writes to newly allocated blocks, limits per‑function writes to 10,000 entries, and emits debugger scripts (Ollydbg/WinDbg) that restore IAT entries and API calls. Works on real malware samples (recovers ~1,000+ API calls) but is slow (minutes) and fails on VM‑based virtualization and when Pin is detectable.
AI-written summary · about
chapters (13)
- 0:00Start
- 1:33API Obfuscation Example
- 2:23Run-time API Obfuscation
- 6:30Monitoring API obfuscation Process
- 9:48How to identify API calls?
- 11:20Memory Access Analysis
- 13:20Building Memory Access Analyzer
- 13:58OEP Detection
- 15:15Identifying Obfuscated API Call
- 16:47Resolving Obfuscated API Call
- 18:45Implementation
- 20:27Limitation
- 21:32Future Work
related talks
 45m"Advanced Malware Threat: handling obfuscated code using..."
 22mTackling runtime-based obfuscation in Android with TIRO
 55mHiding PIN's Artifacts to Defeat Evasive Malware
 40mDynamic Binary Instrumentation Techniques to Address Native Code Obfuscation
 59mFlying blind? - The case for API Security and Observability
 29mEndoscope: Unpacking Android Apps with VM-Based Obfuscation
 26mAn Effective Approach to Software Obfuscation
 20mBluePill: Neutralizing Anti-Analysis Behavior in Malware Dissection