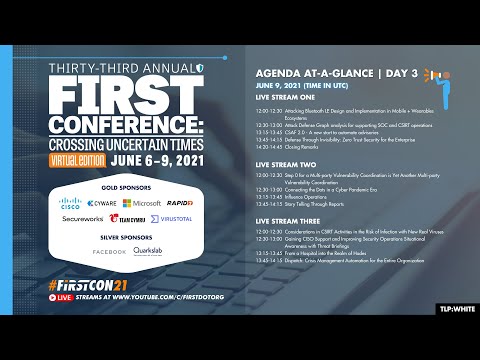
FIRSTCON21 - June 9 | Stream 1 (12:00-14:45 UTC)
summary
Demonstrates that Bluetooth LE “Just Works” pairing lets an attacker recover keys and decrypt wearable data: researchers sniff live traffic with Ubertooth One and Wireshark, feed captures to Crackle, and recover the LTK to reveal step counts and calories in the demo. Shows mobile apps can still expose decrypted BLE attributes to any app with Bluetooth permissions, and that the device only stays safe when protected by app-level encryption and shifted-left secure development.
AI-written summary · about
chapters (6)
- 0:00Start
- 2:20Attacking Bluetooth LE Design and Implementation in Mobile + Wearables Ecosystems
- 28:12Attack Defense Graph analysis for supporting SOC and CSIRT Operations
- 1:16:57CSAF 2.0 - A New Start to Automate Advisories
- 1:43:39Defense Through Invisibility: Zero Trust Security for the Enterprise
- 2:26:20Closing Remarks
related talks
 24mAttacking Bluetooth LE Design and Implementation in Mobile + Wearables Ecosystems
 51mBluetooth Hacking: Tools And Techniques
 43mWhen encryption is not enough: Attacking Wearable
 30mUnfit Story of Fitness Trackers: Hacking BLE Fitness Trackers
 25mSweynTooth: Unleashing Mayhem over Bluetooth Low Energy
 30mUnfit Story of Fitness Trackers: Hacking BLE Fitness Trackers
 18mBLESA: Spoofing Attacks against Reconnections in Bluetooth Low Energy
 06mEvery Byte Matters: Traffic Analysis of BluetoothWearable Devices