Hacking Exposé Too: Just How Transparent is TDE?
summary
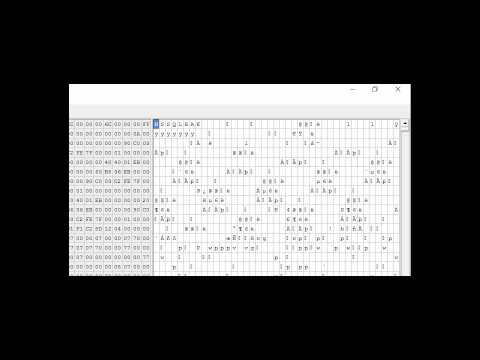
Demonstration shows rawcap and Wireshark capture plain SQL queries and email rows in transit, and a hex editor (XVI32) reveals plaintext credit‑card fields inside unencrypted MDF and backup files. Compressed backups hide strings but still restore; attempting to restore a TDE‑protected backup fails without the certificate. Conclusion is crisp: TDE protects data at rest (MDF/backup/transaction files) but not data in motion, it encrypts backups so hex looks like gibberish, and it adds tempdb overhead (commonly ~3–4% CPU).
AI-written summary · about
chapters (30)
- 0:00Introduction
- 1:20QA
- 2:14Sponsors
- 2:50Pathum
- 5:02Big of the Hour
- 5:28Welcome
- 5:45Agenda
- 7:17Chris Bell
- 8:01What is Hacking
- 9:01Tools
- 16:30Backups
- 17:59Backup Files
- 19:21Search
- 25:34Compress Backup
- 27:17Restore Compressed Backup
- 29:00Transparent Data Encryption
- 32:27Enabling TDE
- 34:47Creating Database Encryption Key
- 36:12Database Encryption Status
- 38:16Turning Off Encryption
- 39:00TempDB Encryption
- 41:47Data at Rest
- 43:35Uncompressed Backup
- 44:39Attempting to Restore
- 47:05Encrypting the Temp DB
- 47:36Increased Overhead
- 48:50Backup Keys and Certificates
- 49:29Backup Compression
- 50:59Final Notes
- 51:41Quick Review
related talks
 48mGetting To Know SQL Server Encryption Capabilities
 47mData at Rest Encryption Going Beyond the Basics to Address Modern Attacks
 51mWhere should I be encrypting my data
 41mSimulation Hacking, the Good, Bad and the Ugly
 47mCunning With CNG: Soliciting Secrets From Schannel
 57mSomething Something Security
- 51mWhere should I be encrypting my data
 48mProtecting the confidentiality and integrity of your high value data with Azure SQL and SQL Server 2