Getting the Balance Right: GDPR and Google Analytics
summary
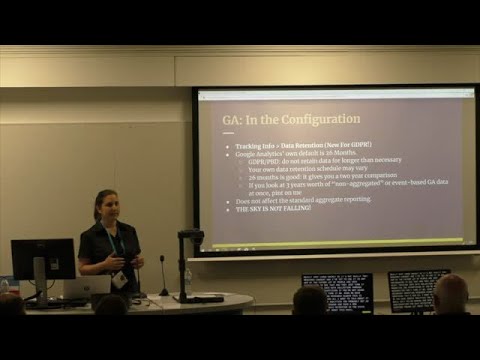
Practical checklist for GDPR-compliant analytics: use Google Tag Manager, set anonymize IP to true, remove any emails or PII from URLs before they reach Google Analytics, keep data retention 26 months (or shorter) and disable User ID, advertising features and remarketing unless active consent exists. Prefer session-only cookies or delete client IDs to avoid long-term tracking. The Google Analytics Deletion API now exists for targeted erasure, and strict tag governance prevents accidental cross-platform profiling.
AI-written summary · about
chapters (19)
- 0:00Start
- 1:50What we're going to cover
- 2:46The European privacy overhaul
- 5:06Definitions: personal data
- 7:01Definitions: controllers and processors
- 7:38Individual rights
- 8:44GA & GDPR: who is who?
- 10:46What does that mean for active consent?
- 13:39So what's the best thing to do here?
- 15:50GA: IP Address
- 17:38GA: In the Page Path
- 20:06GA: In the Configuration
- 26:42GA: With Custom Dimensions & Events
- 30:41GA: Google Tag manager
- 31:40GA: Deletion API
- 32:42Privacy notices
- 34:23Analytics Google Analytics
- 40:53The ePrivacy Directive revamp
- 42:15Resources