Security Testing Tools: Can I Touch You There?
summary
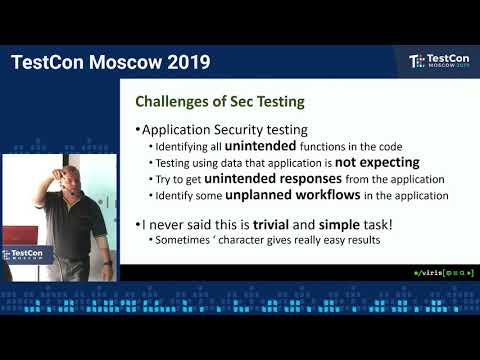
Claims concrete results: 20% of issues discovered by automated tools and 15% detectable with only a browser, with many remaining low/medium findings that testers can eliminate early. Practical tooling includes Burp ZAP Charles OWASP Top 10 and Mobile Security Framework, Dockerized vulnerable apps (DVWA et al.) and labs like Hack The Box for hands‑on practice. Integrating scanners into CI/CD and using dependency checkers reduces noise so pen tests can focus on critical flaws.
AI-written summary · about
chapters (27)
- 0:00Security testing introduction
- 1:11Developer to ethical hacker
- 2:22Software vs pen testing
- 3:26Security flaws in apps
- 5:56Why security testing is not as hard as it seems
- 7:01Talk motivation and results
- 8:47Why security testing matters
- 10:12Security testing challenges
- 13:25Testers lack security skills
- 14:29Testers in app security
- 15:56Criminal mindset for testing
- 17:43Web app security issues
- 20:30Security vulnerabilities examples
- 22:37Thinking outside the box
- 23:19Talk title explained
- 24:23Start security testing
- 27:11Top 10 security issues
- 28:15Web app security tools
- 31:02IoT/serverless security
- 32:05Browser security tools
- 33:14Bug bounties platforms
- 34:14Vulnerable apps for practice
- 35:41Learning security resources
- 37:08Ecosystem security education
- 38:36Security in development lifecycle
- 39:43Security career opportunities
- 40:25Q&A: Convincing product owners
related talks
 38mCan I Touch You There? Tools and Techniques for Security Testing
 27mHow to Start Security Testing Without Fear
 52mApplication Security at DevOps Speed and portfolio scale
 44mApplication Security: Everything we know is wrong
 45mBringing Security Testing To Development: How To Enable Developers To Act As Security Experts
 31mPenetration Testing in the Release Pipeline
 45mAutomated Security Testing in a DevOps world
 37mDeploying Security Testing Practice in Your Team and Company