JFrog Xray to Secure Red Hat OpenShift
summary
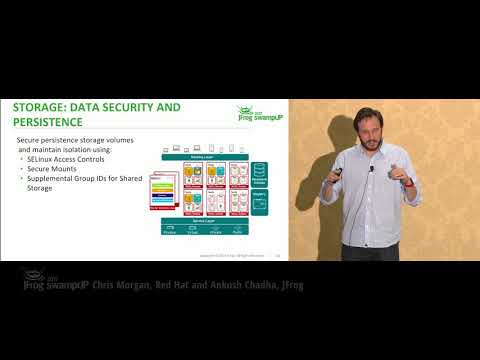
Demonstrates JFrog Xray scanning Artifactory-stored images and dependencies and enforcing policies in OpenShift and s2i/Jenkins pipelines: a demo image shows 4 issues (two RPM, two NPM) including a critical NSS vulnerability; Artifactory blocks downloads of the vulnerable image and s2i builds fail builds when dependencies are flagged. The team fixes the NSS package in the base image, rebuilds, and the pipeline succeeds, proving the component-graph impact analysis plus enforcement works end-to-end.
AI-written summary · about
chapters (8)
- 0:00Introduction and speakers
- 1:29OpenShift overview and architecture
- 3:56Container security fundamentals
- 13:25Artifactory and S2I integration
- 17:21Xray’s role in container security
- 27:39Live demo: Xray enforcement policies
- 39:19Policy enforcement and developer workflow
- 41:28Q&A and closing remarks
related talks
 07mJFrog Sponsored Session - Narasimha Pai, JFrog
 18mGlobal security at maximum velocity: Multi-Region and hybrid DevSecOps
 36mJFrog Platform Innovation: Reloading Development Teams
 01h 13mAddressing the Software Explosion
 29mFrom Vulnerabilities to Vigilance
 09mSpotlight on a New Feature of the JFrog Platform
 01h 29mDevOps 101 Workshop
 08mAll About Dependencies