Anatomy of a Phishing Campaign

summary
July 2025 attackers stand up pypj.org transparent proxy that relays credentials and TOTP in real time, harvest emails from package metadata, and within hours compromise four compromised accounts and upload malicious releases to num2words 0.5.15/0.5.16 containing a Windows DLL scavenger loader that executes on import The proxy produces valid session cookies lasting ~8 hours Traditional TOTP is phishable while WebAuthn blocks proxy Response takes weeks to fully takedown and November defenses add email verification for new-device TOTP logins and note a September 2025 follow up against pypi-mirror.org
AI-written summary · about
chapters (21)
- 0:00Introduction to PyPI security challenges
- 1:51Why attackers target package repositories
- 3:34How the phishing email was crafted
- 5:39The proxy attack mechanism explained
- 7:23Timeline of the incident response
- 9:52Challenges with vendor abuse reporting
- 10:53Malware payload in num2words package
- 13:43Why pinning versions matters
- 15:28Mandating 2FA for PyPI maintainers
- 17:11Why WebAuthn is better than TOTP
- 18:35Actions taken to mitigate the attack
- 20:46Second phishing campaign with PyPI mirror
- 21:30Practical steps to protect yourself
- 23:53The reality of phishing-resistant security
- 24:55Call to action for ecosystem support
- 25:16Q&A: Insights on the attackers
- 26:19Q&A: Trademark use against domain abuse
- 26:39Q&A: Package download impact analysis
- 27:20Q&A: Secure dependency management
- 28:46Q&A: Funding for PyPI security
- 29:50Q&A: Insights on attacker profiles
related talks
 49mBeyond Takeover: Attacker’s in. Now what?
 40mGet Rich or Get Hunted Trying: Uncovering Large Scale Fraud Operations
 58mCatching Transparent Phish: Understanding and Detecting MITM Phishing Kits
 29mHook, Line, and Tinker: A Dive into Phishing Campaign Sites
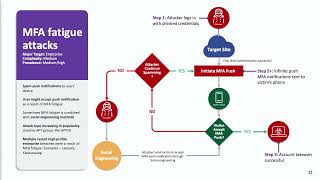 49mThe Death of Conventional MFA: How AiTM Attacks Are Changing the Game
 26mTechnical Tracks
 41mMuraena: The Unexpected Phish
 43m"A rootkits writer’s guide to defense"