Modern And Secure IAM For Modern Applications
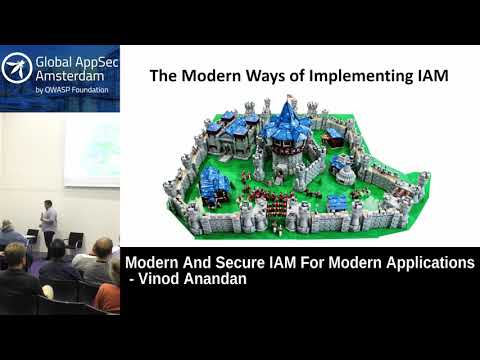
summary
Argues for a central federated IAM instead of per-app auth and names OpenID Connect and JWT for identity tokens, PKCE for public clients and FIDO2 for phishing-resistant, public‑key logins. Cites studies: 81% of breaches involve stolen or weak credentials, 91% of attacks target credentials, 73% password reuse. Recommends reuse of certified providers (Keycloak, IdentityServer), shows discovery endpoints and a live FIDO2 registration that produces a public key and works end to end.
AI-written summary · about
chapters (26)
- 0:00Intro
- 0:27Identity
- 3:10Secure IAM
- 3:52Studies
- 4:26NIST
- 4:50Application Security Verification Standard
- 5:10Traditional IAM
- 6:15Modern IAM
- 9:44OpenID
- 10:26OpenID Foundation
- 11:25JSON Web Token
- 15:09Authorization Code Flow
- 16:36Discovery End Point
- 17:01Public Key
- 17:18SAML
- 19:01Benefits
- 20:29Certification
- 22:13Custom Implementation
- 22:54FIDO
- 23:31Public Key Cryptography
- 24:00Different Protocols
- 24:24Phishing
- 24:56Forms of Authenticator
- 25:27Demo
- 27:19FIDO Server
- 28:29Questions
related talks
 37mCustomer Identity for Modern Apps and APIs
 40mModern Identity Management
 01h 12mIdentity 2.0: the what, why and how of social and federated login
 45mModern Identity Management in the Era of Serverless and Microservices
 35mIdentity and Access Management for the Decade Ahead
 51mYou Shall Not Password: Modern Authentication for Web Apps
 55mYou Shall Not Password: Modern Authentication for Web Apps
 21mEarning Trust in Identity at Scale