Open Source License Compliance and Ory Open Source

summary
An audit finds Ory’s codebase “clean” within the limits of automated tools, using FOSSTology scan to show almost all files under Apache 2.0 with permissive components (some MIT and CC BY 2.5), and a lone copyleft artifact in Swagger Codegen CLI 2.2.3 jar reported removed and not in production. Vendors distributing Ory must comply with Apache 2.0 obligations (copyright notices, license text), treat browser JS and container images as distribution, and build a bill of materials, extract notices, and compile legal notices or run an open source program office.
AI-written summary · about
chapters (13)
- 0:00Intro
- 1:45Use-Cases of Open Source Software
- 2:33Using Open Source in Products and Applications
- 3:26Using Ory Open Source in Products and Applications
- 4:06Vendor Concerns (Your Concerns)
- 5:13Open Source Audit of Ory Open Source [1] [2]
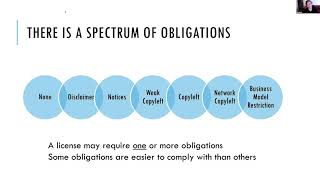
- 6:52Open Source License Categories
- 8:02What Constitutes Binary Distribution?
- 10:07Permissive License Obligations
- 11:16License Compliant Delivery Workflow
- 12:50Open Source Program Office
- 13:43What Do You Need to Get Started?
- 14:38Legal Notices 1/2
related talks
 33mORT Automate compliance using Open Source & InnerSource
 33mThe Cathedral, the Bazaar, and the Coffee House
 30mORT: Automate your open source policy using Open Source & Inner Source
 26mThe FOSSology Project – Open Source Software for Open Source License Compliance
 26mThe FOSSology Project – Open Source Software for Open Source License Compliance
 01h 38mOpen Source Licensing: Types, Strategies and Compliance
 45mOSS License Compliance for Software Developers, NOT for Legal Experts
 50mRunning a Successful Open Source Project