What You Need to Know and Do about Vulnerability Disclosure
summary
OpenSSF Vulnerability Disclosure WG recommends a 90-day disclosure timeline, a 3–5 person vulnerability management team for triage, and use of a simple security.md plus a runbook, templates and GitHub Security Advisories to coordinate response. Process includes reproduction steps, CVE request, patching and concise public advisories listing affected versions and mitigations; embargoes are optional and complex. Guide claims this reduces user risk and warns against launching a bug bounty before hardening and processes are in place. CVE
AI-written summary · about
chapters (9)
- 0:00Start
- 1:52What is vulnerability disclosure?
- 2:07Vulnerability disclosure models
- 3:25Why a whole working group?
- 4:54Why CVD as a recommendation?
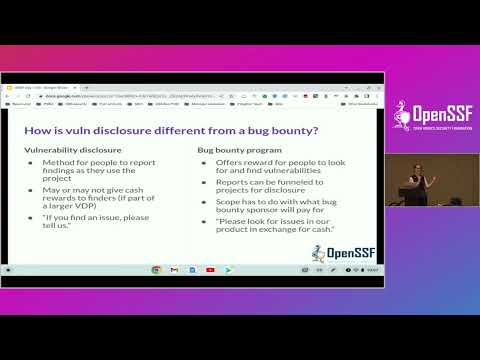
- 5:49How is vuln disclosure different from a bug bounty?
- 11:09Assessment
- 11:50Patching
- 12:5390 day disclosure timeline
related talks
 01h 08mPreparing for Zero-Day: Vulnerability Disclosure in Open Source Software
 44mPreparing for Zero-Day: Vulnerability Disclosure in Open Source Software
 45mSimplifying Coordinating Vulnerabilities & Disclosures in Open Source...
 48mHow to report a vulnerability: Responsible Disclosure for Developers
 13mManaging Vulnerabilities in Open-Source Dependencies
 27mThrough the Looking Glass: How Open Source Projects See Vulnerability Disclosure
 52mAnatomy of a Vulnerability Response - A View from the Inside
 39mSecurity Advisory Programs: Creating Transparency Along the Software Supply Chain