Another year of HackerOne statistics
summary
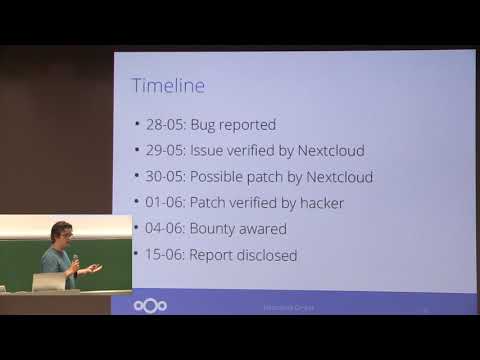
Over the last 12 months hackerone project shows 167 closed reports but only 36 are valid bugs, 16 qualify for bounties, total payouts about $2,300 with median $100 and average $142. Example: a file access control bug allows unauthorized previews, is reported May 28, is reproduced May 29, a patch is ready the next day, is verified and paid in early June, release fixes two weeks later and is disclosed. Program yields actionable reports and fast triage and patching.
AI-written summary · about
chapters (6)
- 0:00What is HackerOne
- 0:21Main purpose of HackerOne
- 1:20Bounty
- 1:57Security issues
- 2:35Perc report
- 3:35Conclusion
related talks
 43mHard Knock Lessons On Bug Bounties
 30mDoes Public Disclosure of Vulnerabilities Affect Hacker Participation in Bug Bounty Programs?
 45m2014.10.29 - Security@Scale - Katie Moussoris, HackerOne
 25mHacker-Powered Data: Why the Most Common Vulnerabilities Aren’t What You Think They Are
 26mLife of a Bug (an insight on the GitHub bounty...
 37mFrom DevSecOops to Security Success: The Bug Bounty Effect at FINN.no
 31mData Driven Bug Bounty
 55mYour License for Bug Hunting Season