Multi-key FHE and Spooky Encryption

summary
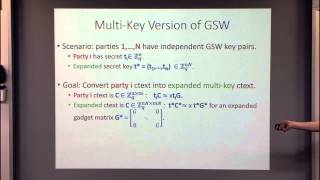
Defines multi-key FHE that converts per-user GSW ciphertexts (all reusing a public matrix B) into a single expanded ciphertext under a concatenated secret so homomorphic ops work across users, and shows distributed decryption as per-user inner products that sum to the plaintext. Key technical gadget: publish GSW encryptions of the encryption randomness so one can homomorphically form the unmasking matrix D; yields two-party spooky FHE (secret-shared outputs) and two-round MPC; general n-party spooky uses a GMW-style compilation.
AI-written summary · about
chapters (11)
- 0:00Start
- 5:52Background on Multi-Key FHE
- 17:48Physical Analogy
- 23:24Multi-Party Computation
- 27:31GSW FHE: Encryption
- 29:25The GSW FHE: Evaluation
- 31:40Homomorphic Circuit Evaluation Noise grows during homomorphic evaluation
- 32:23Multi-Key Version of GSW
- 35:44Ciphertext Expansion
- 44:23Distributed Decryption
- 50:15Spooky FHE: 2 to N parties
related talks
 28mTwo Round MPC via Multi-Key FHE
 45mFully Homomorphic Encryption I
 01h 04mFully Homomorphic Encryption II
 54mFully Homomorphic Encryption
 23mBootstrapping Homomorphic Encryption via Functional Encryption
 01h 07mLattices and Encrypted Computation
 47mHomomorphic Encryption
 40mIt’s a Kind Of Magic: Computation on Ciphertexts