How Secure is Your Base Image? ...
summary
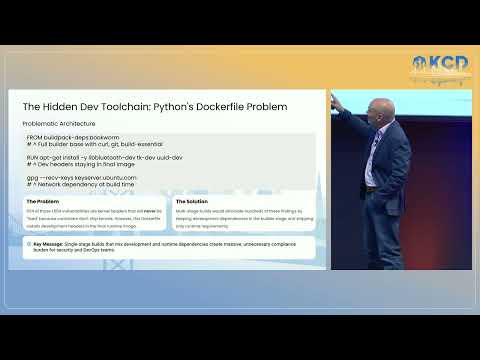
Scans of three common base images (Golang, Python 3.10, and an MCP gateway) reveal concrete problems: a Golang image shows massive accumulated CVEs with 3 criticals, 148 highs and 687 kernel-header-related entries, Python 3.10 reports ~254 high/critical issues, and the MCP gateway hides few but severe flaws (buffer bleed, firewall rule exposure, secret leakage). Scanning uses container pulls, jq parsing and CVE databases; Dockerfiles reveal world-writable GOPATH, retained dev headers and running as root, and a Docker-in-Docker setup with socat and docker CLI. Fixes: multi-stage build, remove dev toolchain, backport or patch git CVE, bump Go/Docker versions, or use a sidecar.
AI-written summary · about
chapters (19)
- 0:00Introduction
- 1:04Base image security matters
- 2:06CISA KEV and Git CVE case
- 3:31Evaluating base images security
- 4:56Three problematic images
- 6:39Golang base image deep dive
- 8:26Golang Dockerfile flaws
- 9:52Golang analysis takeaways
- 10:13Python 310 base image analysis
- 11:39Python Dockerfile vulnerabilities
- 12:22Python image structural issues
- 13:04MCP gateway container analysis
- 14:09Fewer CVEs can be dangerous
- 14:50Docker-in-Docker insecure patterns
- 15:54Remediation strategies
- 16:38Fixing Git CVE and MCP
- 17:41Secure Docker builds best practices
- 18:49From detection to remediation
- 19:30Summary
related talks
 29mDay in the Life of a Base Image: The Evolution of Vulnerabilities in the Most Popular C...
 35mSecuring Containers by Breaking In
 33mBuilding Images For The Secure Supply Chain
 47mSecuring Containers By Breaking In
 16mUnpacking Open Source Security in Public Repos
 38mSo. Many. Vulnerabilities. Why are containers such a mess...
 25mMy Container Image has 500 Vulnerabilities, Now What?
 34mUnpacking Open Source Security in Public Repos & Registries