Security in the Medical Internet of Things
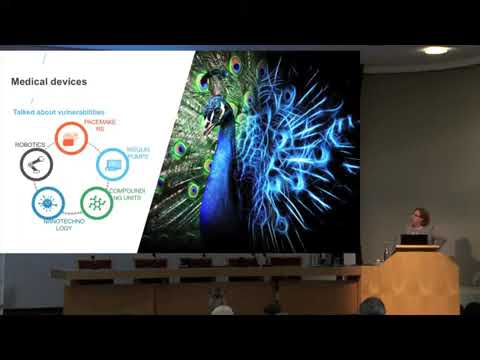
summary
Healthcare cyber security lags other industries and current IoT medical systems routinely expose simple vulnerabilities: hard-coded passwords, open ports 20/23/843 and Bluetooth-enabled devices that sit on hospital corporate networks. Proof-of-concept exploits show insulin pumps and pacemakers can be reprogrammed to deliver lethal doses; a smart pill that transmits via stomach-acid power to a skin receiver and phone highlights new attack surfaces. Regulators issue FDA advisories, EU and MH guidance trails, and constrained device hardware plus legacy protocols compound the risk.
AI-written summary · about
chapters (9)
- 0:00Medical IoT security intro
- 1:57Core security principles
- 3:45Digital health wearables
- 8:18Home IoT vulnerabilities
- 10:07Hospital device flaws
- 12:39Automotive IoT lessons
- 14:04Medical device hacking risks
- 15:08Regulatory gaps standards
- 17:14Call to action
related talks
 01h 01m(In)Security of Medical Devices
 51mSecuring Medical Devices—When Cyber Really Is a Life and Death Issue
 13mThe Future of Cyber Security pt.2
 58mMedical Device Security
 29mSecuring IoT/OT Against Modern Threats
 45mTraceability In Cyber Security:Lessons Learned From The Medical Sector
 51mClosing Keynote - Digital Disease: How Healthcare Cybersecurity Challenges...
 40mInto the Mind of an IoT Hacker | How to Protect IoT Networks & Devices