V1 Bounty: Building A Coordinated Bug Disclosure Bridge For The EU
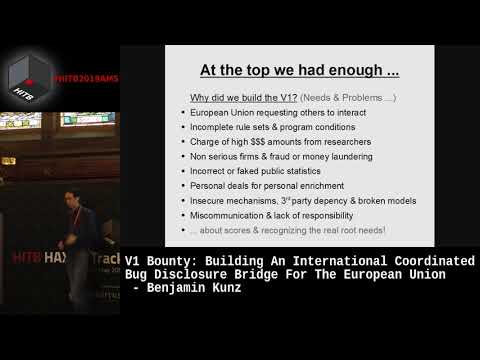
summary
A coordinated EU–Asia bug bounty bridge is built: a V1 Bounty platform using the Amber framework, hosted in Germany (Frankfurt) and designed to be GDPR|DSGV compliant. It centralizes responsible disclosure, adds an encrypted ticketing/store with a master key, a push notification history and leaderboards, and an offline conference mode for local events. It targets inconsistent program conditions and poor tooling by shipping program templates, verification workflows and partner integrations; first programs are going live next week.
AI-written summary · about
chapters (6)
- 0:00Introduction and speaker intro
- 6:47EU’s coordinated disclosure push
- 15:58V1 Bounty platform details
- 27:14Security and transparency features
- 36:59Platform functionality demo
- 47:00Future plans and Q&A setup
related talks
 29mAPI Security Risk Management with Bug Bounties
 11mBuilding a Bug Bounty Program: From the Trenches
 49mBugs on a Plane: Implementing a Bug Bounty in an Airline IT/OT Environment
 50mBug Bounty Programs: Successfully Controlling Complexity and Perpetual Temptation
 55mYour License for Bug Hunting Season
 52mPractical Tips For Running A Successful Bug Bounty Program
 46mHow to run a successful bug bounty programme
 15m"You've Got Your Nice List of Bugs, Now What?" Vulnerability Discovery and Management