The Agile Way to Add Sec, Dev & Ops into Waterfall
summary
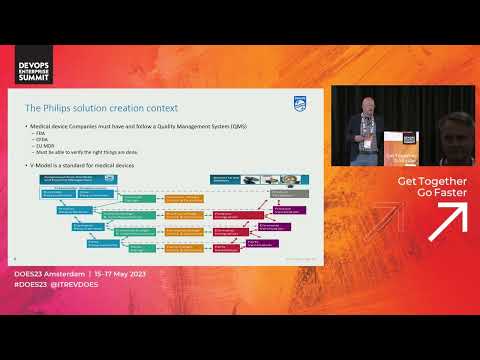
Philips keeps a V‑model medical SDLC but adds targeted agility: automated SCA in CI/CD and an SBOM repository that lets teams trace vulnerable libraries fast, plus semi‑embedded but independent security testers in the pipeline (offshore security ninja team) who reduce final test time. Risk management and choice‑architecture decide releases; ship‑holding rules and regulatory evidence remain, so the approach nudges waterfall toward agility rather than replacing it.
AI-written summary · about
chapters (13)
- 0:00Introduction
- 2:11Philips context healthcare
- 7:00Medical solutions regulatory
- 10:35Regulatory V-model
- 13:01Agile development challenges
- 16:31Security governance threat
- 20:00Regulatory evidence needs
- 22:27Hackers vs corporate security
- 23:54Integrate security DevOps
- 26:45Risk management agility
- 28:10Agility process demands
- 30:20Negotiation testing security
- 31:28Agile quality issues
related talks
 45mAgile Alchemy: Balancing Flexibility and Compliance in Software Development
 44mCan you be agile and compliant?
 46mApplication Security in an Agile World
 40mMoving from the License Raj to Light Touch Agile Governance
 57mAgile Application Security
 13mAgile in Security and Security in Agile
 29mPainless Agile Security
 45mAgile Security Testing - Lessons Learned