MITRE D3FEND
summary
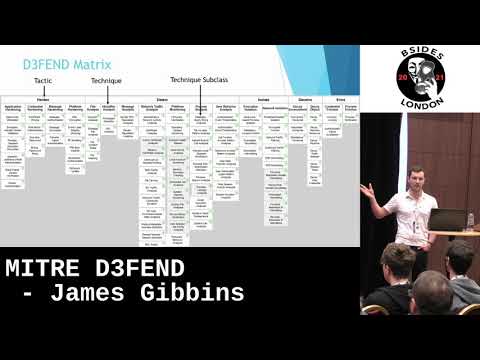
MITRE D3FEND is a defender-focused complement to ATT&CK, currently beta v0.9, mapping over 100 countermeasures across five tactics and linking them to 232 artifacts and concrete offensive techniques. Pages show definitions, implementation notes, and references (eg. NIST SP 800-63-3 for strong password policy). Use cases demonstrated: pick a countermeasure, follow references to harden systems (DEP/NoExecute), simulate attacks with Atomic Red Team to test detection, and deploy deception like honey nets guided by patent and vendor references.
AI-written summary · about
chapters (7)
- 0:00Introduction to MITRE D3FEND
- 1:28Understanding MITRE ATT&CK
- 3:58Overview of D3FEND framework
- 5:03Exploring D3FEND countermeasures
- 7:33Artifacts and their relationships
- 9:40Practical uses of D3FEND
- 12:45Summary and future of D3FEND
related talks
 58mMITRE ATT&CK for Developers
 01h 47mMITRE ATT&CK Fundamentals
 26mA Primer: Getting Started with MITRE Shield
 40mA Primer: Getting Started with MITRE Shield
 30mCybersecurity in the semantic web with MITRE D3FEND
 20mDynamic Defense: Crafting threat models with real-world Intelligence
 39mThe PR3TACK Initiative: Building the World’s First Preemptive Tactics & Countermeasures Knowledgebas
 48mMITRE ATT&CK: The Play at Home Edition