.NET Reversing and Exploitation for Cool Kids
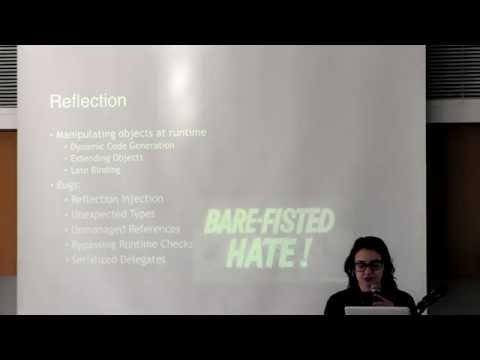
Talkat AppSec California 2015 · on Tuesday, 2015-01-27· at 11:00· Annenberg Community Beach House: Track 1, 415 Pacific Coast Hwy·
summary
Covers practical .NET reversing and exploitation with concrete examples: uses Reflector, CFF Explorer and a hex editor to decompile and edit assemblies, demonstrates a strong-name bypass via registry toggle and replacing a precompiled GAC native image so System.Drawing.Image returns a static payload (demo works), explains a trusted‑chain bug (security exception XML conversion) that yields code execution, surveys five surprising ASLR-misconfigured assemblies, and shows DLL byte patching to alter framework behavior.
AI-written summary · about
chapters (10)
- 0:00Start
- 4:07Microsoft's Answer to Java
- 5:43The Common Language Infrastructure
- 14:48Tammer Detection
- 21:03Reflection
- 24:56Dotnet Security Model
- 25:20How Access Rates Are Determined
- 29:45Global Assembly Cache
- 31:26Security Transparency
- 34:28Dotnet Framework Vulnerability
related talks
 56mHacking .NET(C#) Applications: The Black Arts (ASM attacks)
 01h 06mHow hacking works
 45mFinding Vulnerabilities through Static Analysis and Scripting
 01h 06mHacking C# from the inside
 47mThe Art of Reverse Engineering Flash Exploits
 50mWrite Once, Pwn Anywhere
 02h 18mHacking C# from the inside - how to do anything in .NET
 38mClose Encounters of the Advanced Persistent Kind: Leveraging Rootkits for Post-Exploitation