Future-Proofing Your APIs: A Holistic Approach to Security, Privacy, and ROI.
summary
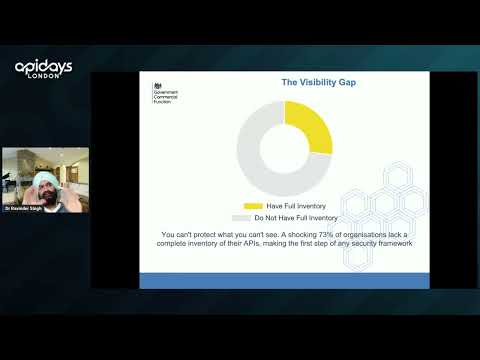
Framework prescribes three pillars—security, privacy, ROI—backed by concrete claims: 73% of organisations lack a full API inventory, broken access control vulnerabilities rise ≈40%, average breach cost ≈$4.4M, and British Airways’ 2020 API incident hit ~400,000 customers and drew a £20M fine. Recommended controls include shift left secure-by-design, SAST/DAST in CI/CD, runtime protection and a centralized API gateway, granular least privilege authorization, data minimisation, encryption in transit/at rest, and AI-driven monitoring across assess→design→automate→manage→monitor.
AI-written summary · about
chapters (11)
- 0:00API future-proofing intro
- 1:07APIs as business backbone
- 2:16API insecurity costs
- 3:19Modern API threats
- 4:42Three pillars for resilient APIs
- 5:47Security: Shift left and stay alert
- 9:04Privacy: Foundation of trust
- 11:11ROI: Cost center to revenue
- 12:59Five-step holistic approach
- 14:47Security, privacy, and ROI integration
- 15:52Q&A
related talks
 58mA Risk based Approach to API Security
 24mAPI Security in DevSecOps: Built-In, Not Bolted On
 22mLayered Approach of API Security Strategies and its Business Impact
 22mThe Ultimate Guide to API Security & Privacy by Design
 16mDo the Right thing, shift Left!
 19mAvoid These API Security Pitfalls: Expert Insights
 24mSecuring the Modern API Ecosystem
 26mAPI and Application Security - The Future