Distributed Zero-Knowledge Proofs and Applications to Secure Computation

summary
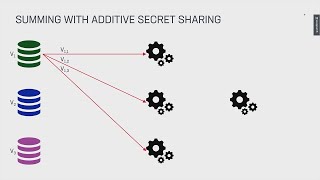
Introduces a construction of fully linear PCP/IOP tools that let a prover give a proof split as additive shares to multiple verifiers, using secret sharing, sumcheck-style low‑degree tests and Fiat–Shamir to get one‑round variants. Claims sublinear proof size (≈√n for degree‑2 predicates, down to log n with interaction) and shows compilers that convert passive MPC to active MPC with sublinear additive overhead — e.g. three‑party single‑corruption costs ~1 element/gate and general honest‑majority achieves about 1.5 elements/gate, works over fields and Zm; small‑field soundness is fixed by moving proofs to extension fields.
AI-written summary · about
chapters (22)
- 0:00Introduction
- 0:55What is secure computation
- 2:03Zeroknowledge applications
- 7:02Motivation of a lighter approach
- 9:12Definitions
- 11:17Application Settings
- 13:25Distributed ZeroKnowledge
- 14:41Agenda
- 16:05Definition
- 18:58Side notion
- 19:25Linear probabilistically checkable proof
- 23:38Interactive oracle proof
- 29:16Building constructions
- 31:05Communication complexity
- 35:43Passively secure protocols
- 37:27Type 1 compiler
- 42:29Type 2 compiler
- 44:22State of the art
- 45:50Dishonest majority
- 47:45The punchline
- 48:16Summary
- 48:55Questions
related talks
 41mGKR based Zero-Knowledge Proofs
 44mIOP based Zero-Knowledge Proofs
 35mEfficient Zero Knowledge Protocols: The Modular Approach
 41mMPC-in-the-Head based Zero Knowledge Proofs
 01h 31mIntroduction to Secure Multi-Party Computation
 26mApplications of Zero Knowledge Proofs in the Banking Industry
 44mBilinear Pairings-based Zero-Knowledge Proofs
 52mDiscrete Log based Zero-Knowledge Proofs