Creating an AppSec Pipeline with Containers in a Week
summary
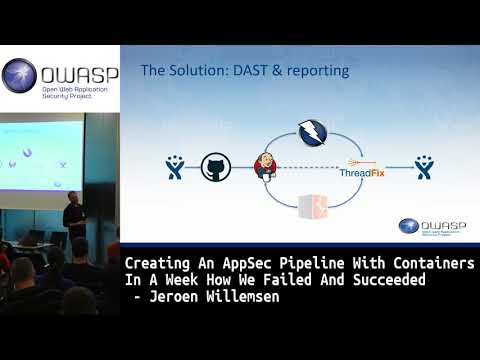
Shows how to build a usable application security pipeline in one week by integrating Docker containers into a Jenkins pipeline. The pipeline runs license and JavaScript checks, container-hardening tools (docker-bench), multiple vulnerability scanners, artifact storage and ticket creation, and adds filtering to reduce noise while surfacing only actionable findings and supporting legacy systems.
AI-written summary · about
chapters (10)
- 0:00AppSec pipeline challenge
- 2:53One-week security
- 5:00Building secure pipeline
- 9:00Security tools
- 13:37Docker security
- 17:47Legacy testing
- 21:41Developer feedback
- 25:12Automation improvements
- 28:46Pipeline scaling
- 32:24Final takeaways
related talks
 42mMaking Continuous Security a Reality with OWASP’s AppSec Pipeline
 43mBuilding a Secure DevOps Pipeline
 46mBuilding An AppSec Pipeline: Keeping Your Program, And Your Life, Sane
 48mAppSec++ Take the best of Agile, DevOps and CI/CD into your AppSec Program
 20mAI-Driven Security as Code in Jenkins
 43mSecurity in DevOps Strategies
 57mWhat’s in an AppSec program?
 39mContinuous Security at the Next Level